Mitigations for CVE-2026-109618 and CVE-2026-109619 that work until you can install the fixed PHP, based on PHP's advisories. Tested configs for nginx, Apache, …
@davidism@mas.to I think so, yeah! Unfortunately the current preview has a few limitations that make it an imperfect replacement for hash-pinning, but I think GitHub intends to have it be a full alternative/replacement for pin bumping/hashing tools in the long term.
Maintainers of open source projects should be mentoring folks to become their replacements. Not just thinking this is about controlling their project.
I have learned this the hard way for gcc.
You can't just think it is your way or the highway. Also gsoc is NOT a replacement for mentoring inside the project. It should supplement the mentoring that is done, just like an internship.
Also this is not unique to gcc, it is many open source projects.
And then there is the gaming of github stats, the one or two commits in llvm and leave issue. Those are used to gain stats for a job.
Seriously open source is broken because of the gaming of the system.
Even inside companies where you have the person with the most open source commits. Or the person who opened the most issue. Or the person who reviewed the most. (What is funny is that i am that person but I am not trying to play the game of counting, I am just trying to push gcc forward).
At the same time I am mentoring folks both inside and outside of qualcomm on both gcc (and even to a less sense llvm) and performance analysis.
But going back to my original point is mentoring and maintainship overlaps. It is not one or the other but rather both in the same role.
By the time you step down you should have at least mentored a few to be able to take you from you. If you have not you partially failed a as a maintainer as the project will no longer can be maintained in the future.
So Linux mainline is going to allow for unbranded AI contributions. Tbh I wonder if this is going to be the test for folks' commitments to anti-AI software b/c y'all about to move to a BSD-like?
🙋♂️ what if one client worked on every forge?
𝔣𝔬𝔯𝔤𝔢𝔰 is a new TypeScript library for issues, PRs, notifications, checks and webhooks across 12 forges ✨
forges.link
kubernetes will commit to no longer using kubernetes because we have had critical vulns. instead, kubernetes will be collaborating with @quinnypig.com to migrate kubernetes to route53.
If your response to this vulnerability is "just don't use PHP lol" I have to assume that you know zero about web development and the web outside of a modern bespoke, FAANG, React/Angular, static site generator type of way and you should probably sit this one out 'cause you look a little dumb
I do not like Chainguard. You cannot get me to say a single positive thing about them as a company. Leaking a critical vulnerability in violation of an embargo is outrageous behavior even for them and they absolutely know better.
My "Lime bikes are not for jousting" t-shirt has people asking a lot of questions already answered by my shirt
https://www.bbc.com/news/articles/c9zrdpg7256yo
There should be some kind of calculator where whenever a billionaire donates some amount of money, you can quickly what percentage that is of their net worth, apply it to your own net worth and see how much of a sacrifice it actually is
I hope the usage of the tag “vibecoding” isn’t what’s putting you off from the site. It’s got a very particular (and contentious) meaning that isn’t really at all attached to what “vibecoding” means in other circles. It‘s basically applied to anything tangentially related to LLM use
😂 fair.
Idk, I worked there 2022-2026. There was definitely a lot of "hey we need to scale" talk, but I think the total amount took a lot of folks off-guard. It's also kinda hard to scale when you're already GIANT.
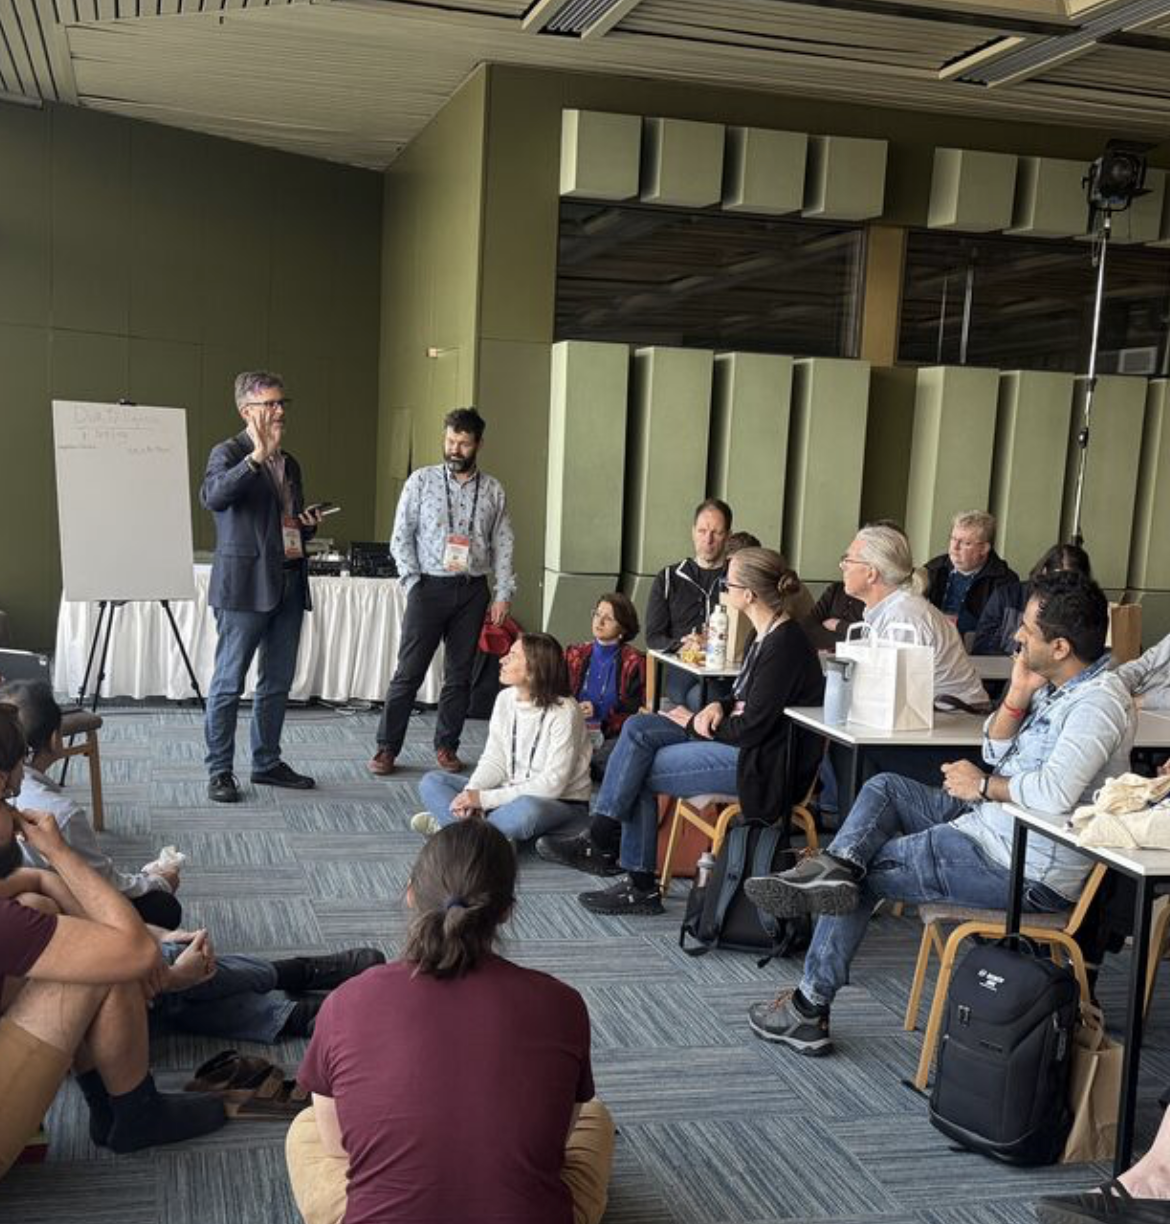
Explore key takeaways from the Alpha-Omega roundtable at OSS EU 2026, featuring discussions on open source cybersecurity, SEIRs, criticality cohorts, and project sustainability.
Since Alexander Skarsgard is a topic right now I want y'all to know one time at DragonCon I went as Felicia from Darkstalkers, and he sent someone across the room to go get me so he could take a picture that he insisted was for his mom. He is weird but in a very charming way.
I have had the displeasure of integrating with a few different APIs over the past few weeks while working to automate Vori’s onboarding flow. These APIs have been for systems including contract rendering and e-signature collection, invoicing/billing systems, CRMs, card processors and gateways, and card terminal providers.
Attached: 1 image
On my way home from Open Source Summit EU in Prague. So much global cyber policy! If the attendance at sessions and workshops is any measure, CRA and how it impacts the open source ecosystem has become a very hot topic. Guides available at https://policy.openssf.org and free training available here https://openssf.org/tag/cra-training-course/ by the way.
 Jamie Tanna
.
#php
#security.